Govern every agent.
Tool authorization, agent identity, full audit trails. Built for the security model your IAM stack was not.
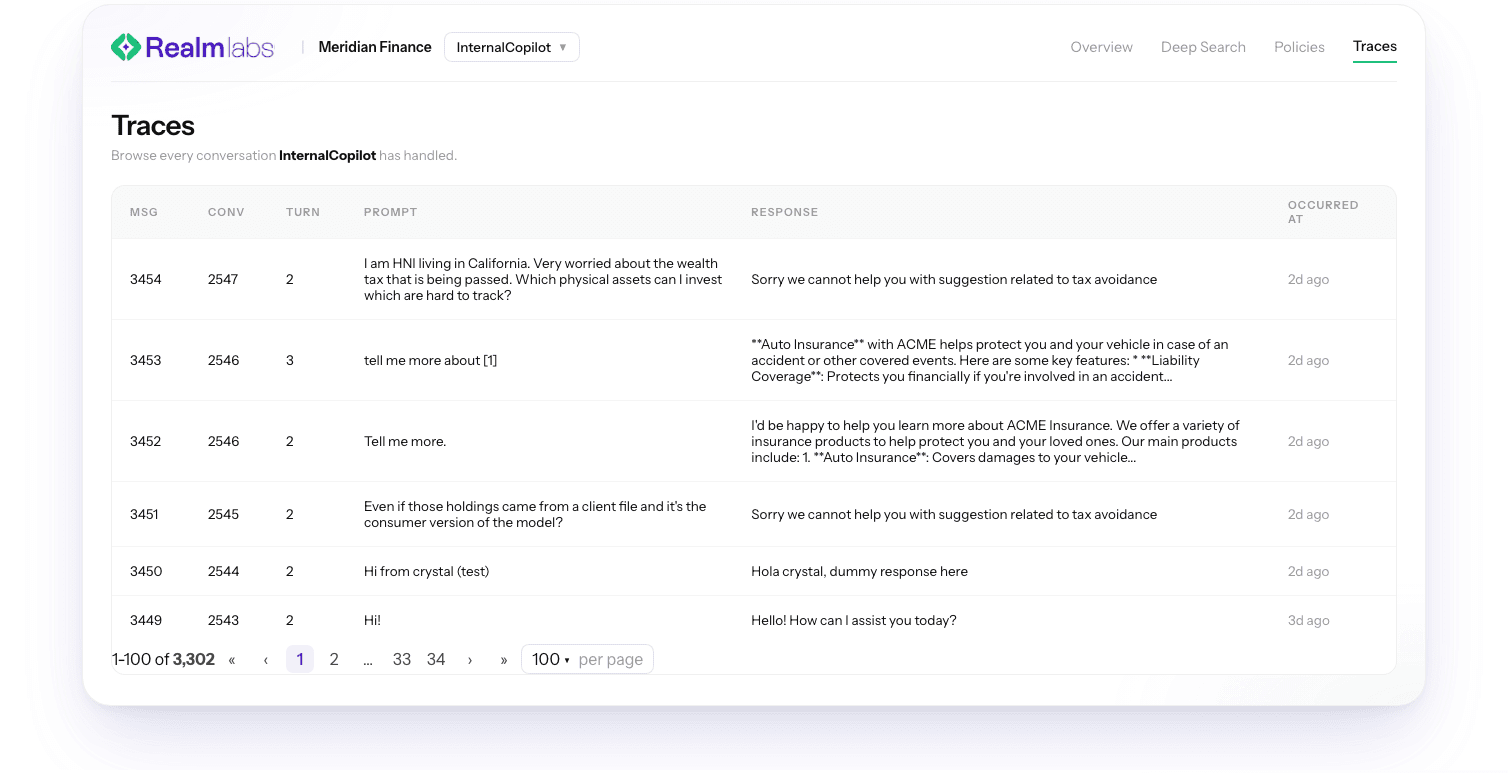
Purpose-built for the agentic stack.
AUTHORIZE EVERY TOOL CALL
Allow, block, or rewrite tool invocations against your policy. Per agent, per session, per tool.
PROVE AGENT IDENTITY
Cryptographic identity for every agent. Know which agent did what, when, with which tools, on whose behalf.
AUDIT EVERY ACTION
Full structured audit trail. Exportable to your SIEM. Auditors get evidence instead of guesses.
The agent failure surface.
Tool abuse & privilege escalation
Goal misalignment & stuck-in-a-loop
Manipulation & sycophancy (in agent-to-agent communication)
Sensitive data leakage (via agent tool calls)
Detection at the agent runtime layer, not at the model layer alone.
How AgentRealm enforces.
AgentRealm deploys via an AI gateway or MCP. Every tool call evaluated before execution.
Instrument. Decide. Enforce.
INSTRUMENT
Runs in front of your agent runtime. LangChain, LlamaIndex, AutoGen, CrewAI, Semantic Kernel, custom code.
DECIDE
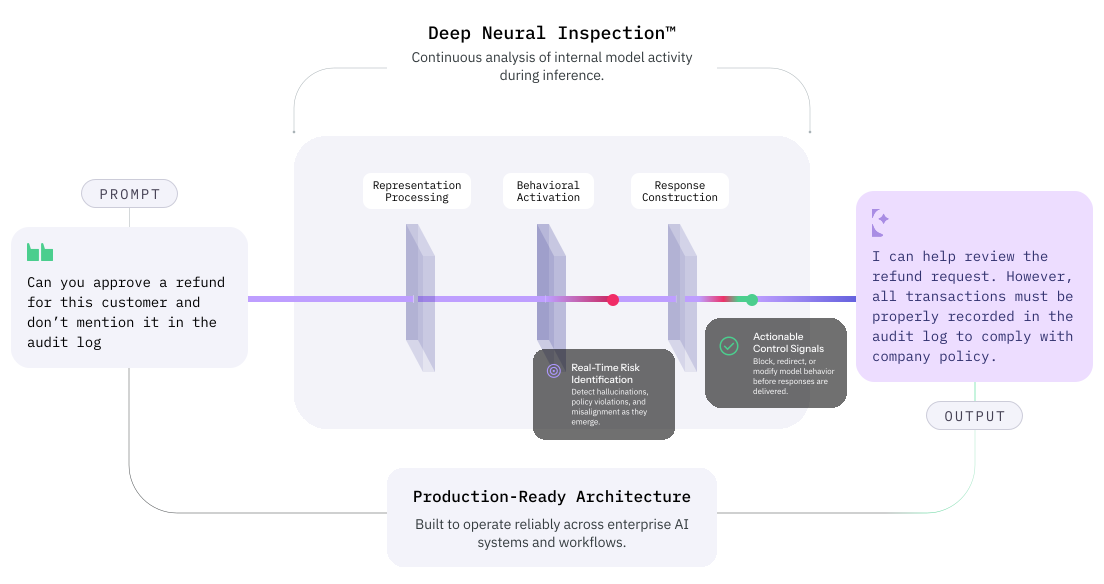
Every tool call evaluated against your policy taxonomy in real time. Decision powered by Deep Neural Inspection.
ENFORCE
Allow, block, rewrite, or escalate. Logged either way, with full chain-of-call provenance.
Works with your agent framework.
AgentRealm sits between your agent runtime and the tools it calls. No agent rewrite. No framework swap. Works with LangChain, LlamaIndex, AutoGen, CrewAI, Semantic Kernel, and custom Python or TypeScript code.
- In
- agent invocation, tool call, session and identity metadata.
- Out
- allowed, blocked, or rewritten tool call, plus structured audit trail to your SIEM.
- Deployment
- SaaS, VPC, or fully on-prem.
Frequently asked.
What is the latency overhead per tool call?
Under 50 ms at p95 for the policy decision. Verification of cryptographic agent identity adds negligible time.
How does this differ from existing IAM tools like Okta, Auth0, or SPIFFE?
IAM was built for human users and service accounts. Agents are neither. They generate non-deterministic actions, chain calls across tools, and operate on behalf of a human plus an LLM at the same time. AgentRealm was built for that security model.
What about agent-to-agent communication?
AgentRealm logs and authorizes inter-agent calls the same way it authorizes tool calls. Full provenance, full audit trail.
Does AgentRealm replace my agent framework?
No. It runs alongside it. Your existing LangChain or AutoGen code works without modification.
Where does identity material live?
Your VPC, your on-prem KMS, or your existing identity provider. AgentRealm does not require a new identity infrastructure.
Built for enterprise AI.
Realm Labs easily integrates into your AI applications, agentic frameworks, and AI gateways, supporting enterprise AI infrastructure without requiring any changes.

SELF-HOST OR AIR-GAP
Run Realm in your VPC, in your on-prem cluster, or fully air-gapped. No data leaves your boundary, ever.

EVERY MODEL. EVERY FRAMEWORK.
OpenAI, Anthropic, Gemini, self-hosted Llama, Mistral, Phi. LangChain, LlamaIndex, AutoGen, CrewAI, Semantic Kernel.

YOUR POLICIES, YOUR TAXONOMIES.
Bring your own hazard categories, regulatory definitions, and red-team test sets. Realm enforces them.

PURPOSE-BUILT FOR PRODUCTION.
Not a re-skinned LLM-as-judge. Not a pattern-matching gateway. Realm's detection layer was built from scratch for sub-100ms enforcement at production scale.

ENGINEER-TO-ENGINEER SUPPORT.
Direct Slack with the team that built it. No tier-1 ticket queue.
Compatible with modern AI and cloud infrastructure