Stop the AI failure. Prove you stopped it.
Catch what your existing tools cannot see. Block the unsafe response in flight. Hand the auditor and the board the receipt.
Three years ago you explained ransomware to the board. Two years ago, supply chain. Last year, identity. This year the question is "what is our AI doing right now, and how do you know?" And for most enterprises, the honest answer is "we don't."
You have an AI gateway. You have model evals. You have a red team. You have a compliance team writing controls that documentation alone won't satisfy. None of them watch the model in production, in real time, on the actual traffic your business runs on. That gap is what gets reported in the next disclosure form. It is also what fails the next audit.
What Realm gives Security and Compliance.
SEE EVERY FAILURE
(Prism)Every prompt and every response, scored against AI failure modes in real time. The 90% your gateway and guardrails miss, surfaced before they show up in user complaints or audit findings.
STOP THE UNSAFE RESPONSE
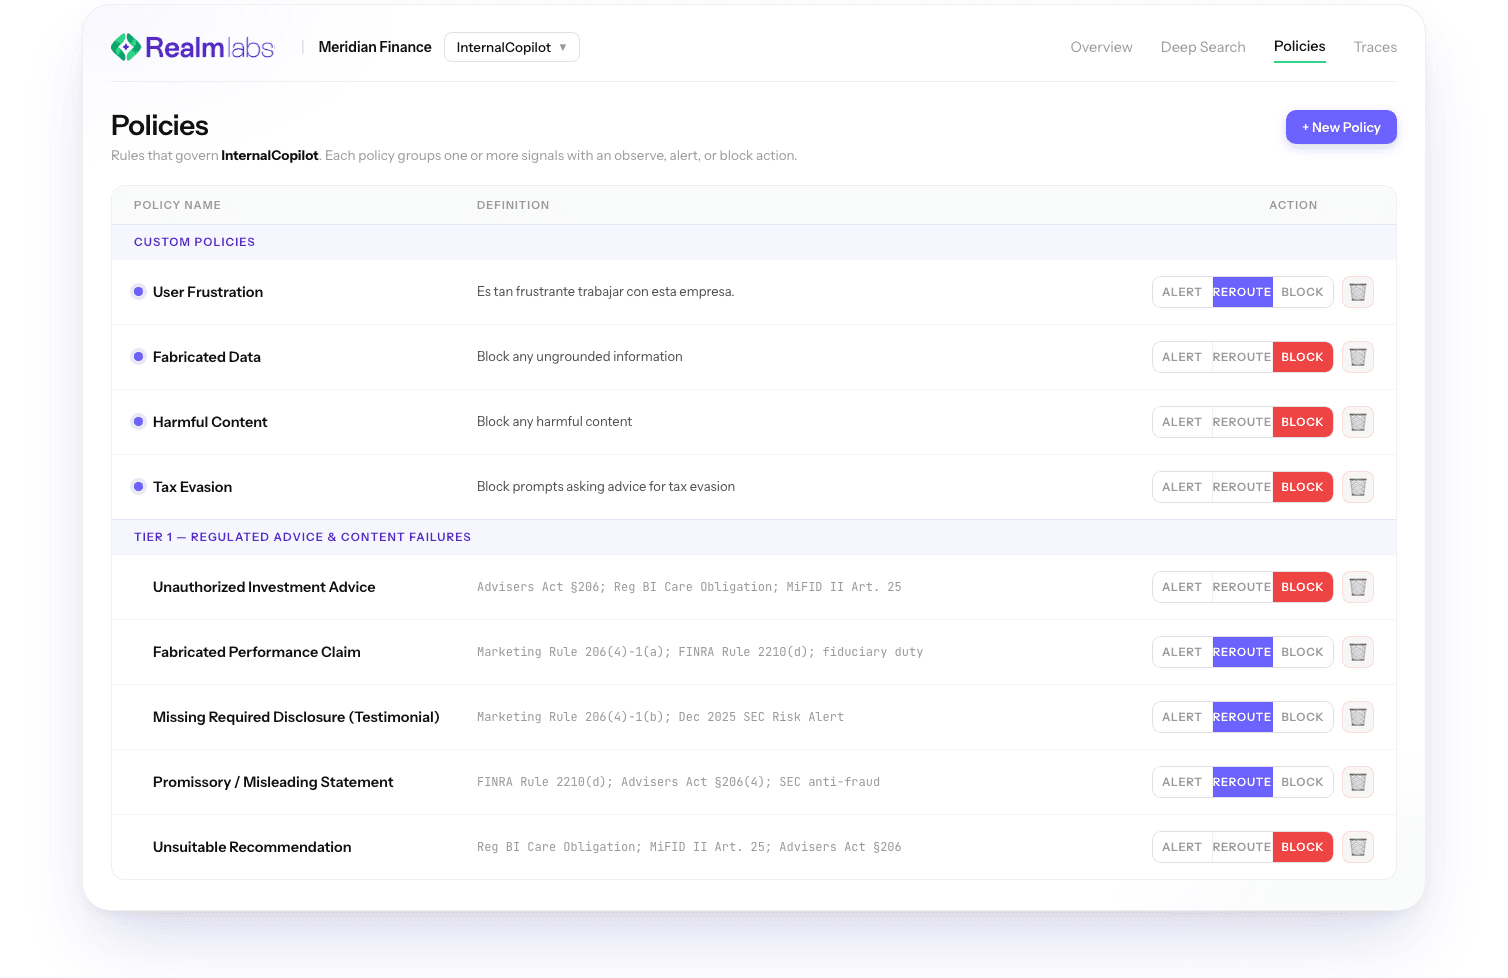
(OmniGuard)Inline blocking against direct and indirect prompt injection, brand and policy violations, sensitive-data exfiltration, harmful content. Powered by Deep Neural Inspection. The only platform that detects and enforces at the model level, not at the input or output string.
HAND OVER THE EVIDENCE
(AgentRealm and across the platform)Per-conversation audit trail with concept-level reasoning per decision. Deterministic and reproducible. Mapped to EU AI Act, NIST AI RMF, ISO 42001, and the OWASP LLM Top 10. The only platform purpose-built to hand your existing GRC framework regulator-grade evidence without translation.
What good looks like for Security and Compliance.
Every prompt, generation, and tool call from every AI app in your environment, in one searchable place.
Real-time enforcement when the model is about to do something it shouldn't, before the user sees it.
A per-conversation audit trail your regulator, your board, and your auditor accept. Mapped to EU AI Act Article 15, NIST AI RMF, and ISO 42001.
How Realm shows up for Security and Compliance.
OBSERVABILITY-OF-RECORD
(Prism)Score every prompt and every response. The audit log + classification system both buyers reference.
DETECTION AND ENFORCEMENT
(OmniGuard)Block prompt injection, brand violations, harmful content, and PII leakage in flight.
AGENT GOVERNANCE
(AgentRealm)Tool-call authorization and audit trail for every agent already running in production.
What Security and Compliance leaders actually ask first.
How does this map to EU AI Act Article 15, NIST AI RMF, and ISO 42001?
Realm produces structured, deterministic, per-conversation evidence covering the model's reasoning, the policy applied, and the decision taken. Designed for the EU AI Act's record-keeping requirements out of the box. Same mapping covers NIST AI RMF and ISO 42001 audit-trail and risk-management controls. Mapping document available under NDA.
Can this run in my environment, not in your cloud?
VPC and on-prem, including air-gapped, are supported deployment options.
How long until I have something to show the board or the auditor?
Most teams have a board-ready failure-distribution report and an auditor-ready per-conversation log within 30 days of connecting Realm to a single AI application.
What happens if Realm is down?
Configurable. Fail-open or fail-closed per policy.
Is the evidence Realm produces admissible in regulatory review?
Realm's evidence is deterministic, reproducible, and exportable in structured format. Whether it's admissible depends on the regulator and the proceeding; Realm's design intent is regulator-grade. Sample audit logs available under NDA.
Stop your next AI failure. Hand over the evidence.
30-minute working demo. Bring your hardest deployment, your toughest auditor question, or both.